Parchemin: Secure, Ephemeral and Zero-Knowledge Secret Sharing
Parchemin is a privacy-first secret-sharing service that lets you send passwords, API keys, private tokens and confidential documents without ever leaving a permanent plaintext trace on email servers, chat logs or support tickets.
How it works
Your note is encrypted directly in your browser using the proven OpenPGP standard before it ever reaches Parchemin's servers. The decryption key lives exclusively in the URL fragment (#), which browsers never transmit — meaning Parchemin literally cannot read your secrets.
Key features
- Zero-knowledge E2E encryption — client-side OpenPGP, key never sent to the server.
- Self-destruction — "burn after reading" mode or automatic expiry from 1 hour to 30 days, after which the encrypted payload is irreversibly deleted.
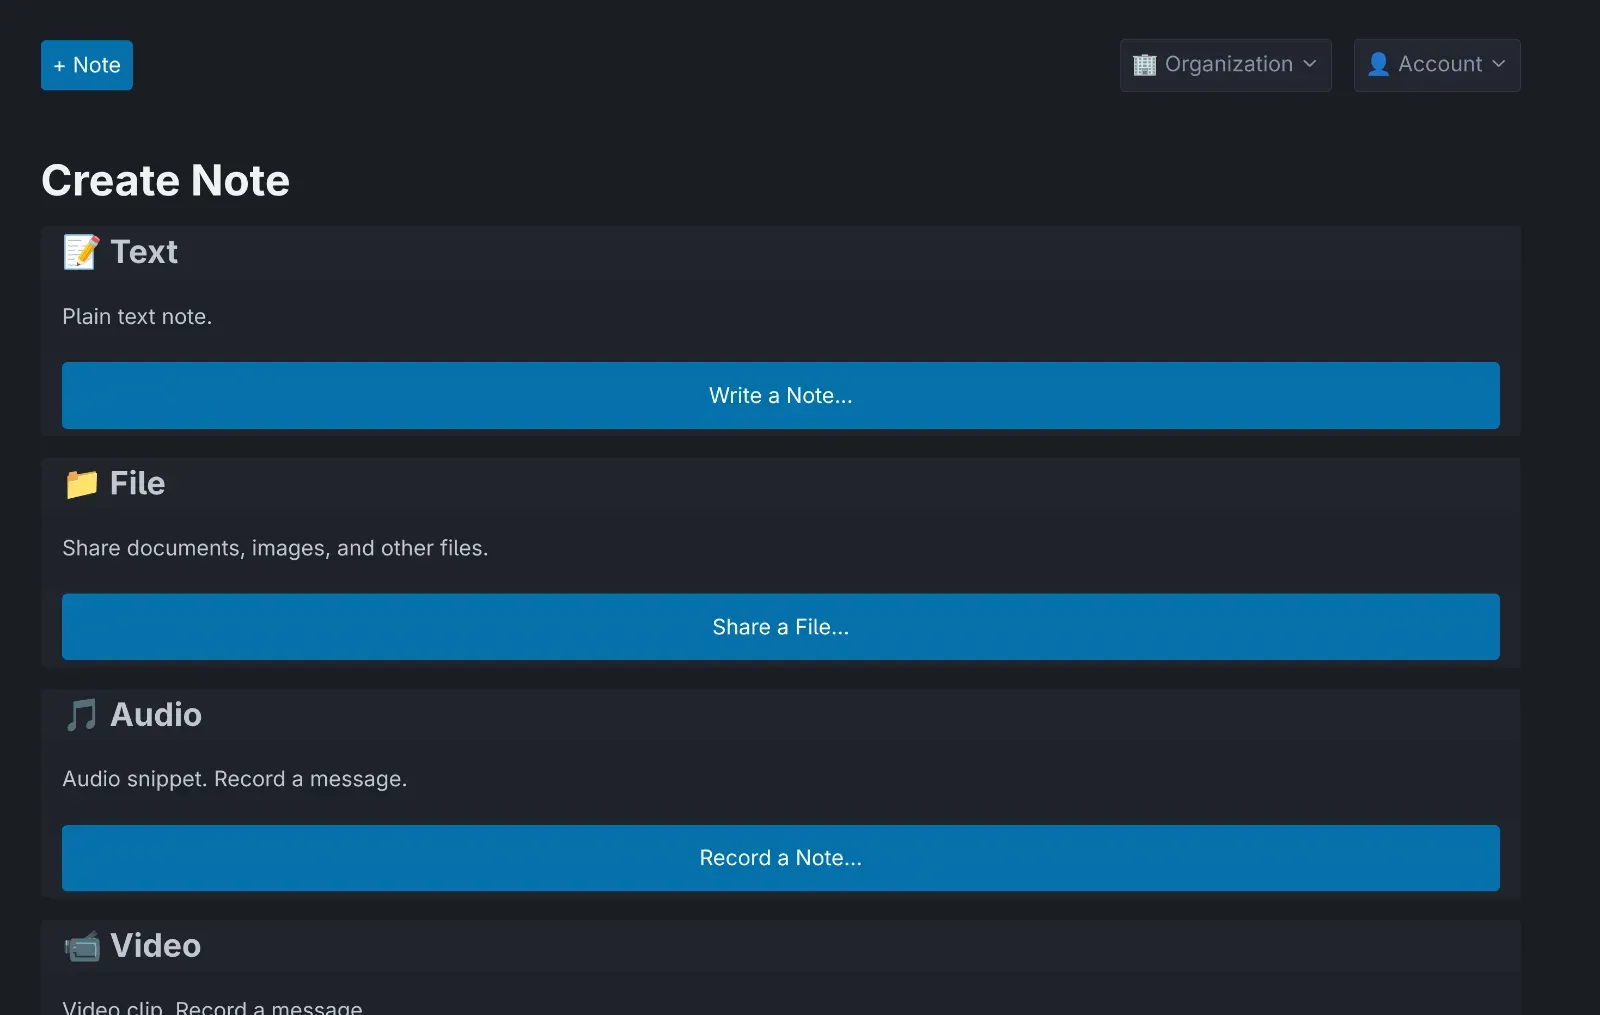
- Multiple content types — send text notes, upload files, or record audio messages.
- 100% ad-free and tracker-free — no advertising, tracking pixels or third-party analytics scripts (unlike legacy tools such as Privnote).
- Built for teams — administrators can enforce compliance guardrails: mandatory expiration caps, required secondary passwords per domain/workspace, and strict single-read rules.
- No recipient account required — anyone can decrypt a note instantly in any modern browser, no sign-up or app install needed.
Primary use case
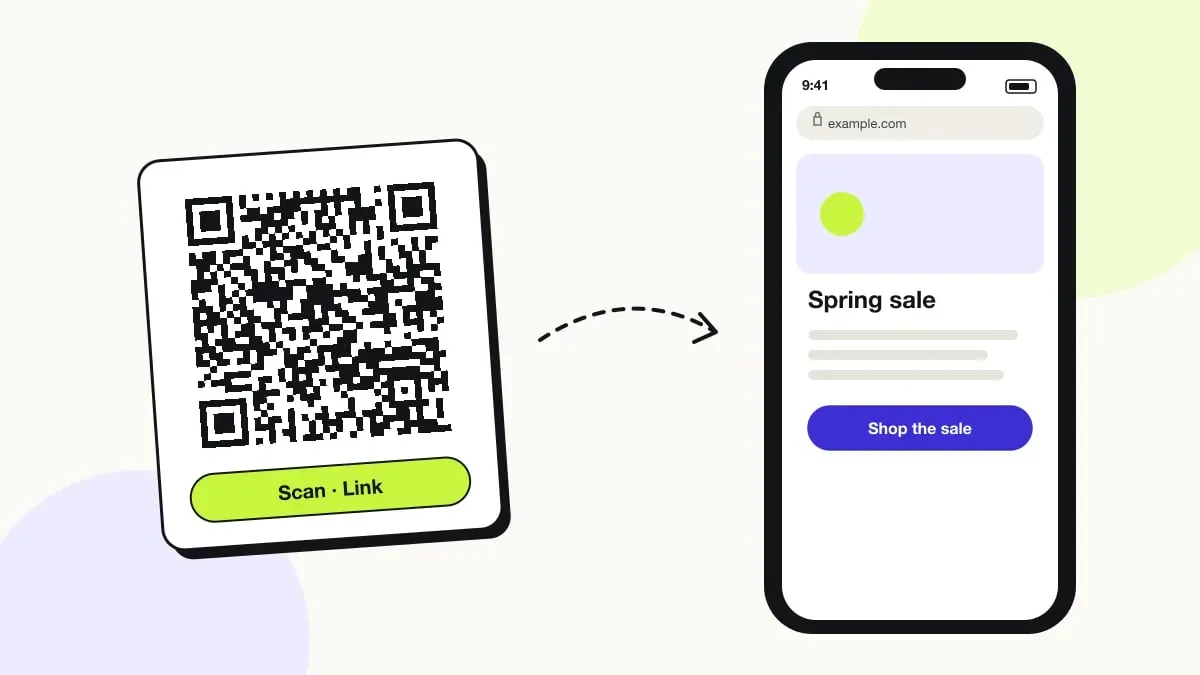
Parchemin is ideal for developers, IT admins, agencies and businesses that routinely exchange credentials with colleagues, contractors or customers and need a defensible, compliant way to do so. Create the note, choose your security options, share the single-use link through any channel, and the content vanishes after it is read.